Community banks and credit unions balance personal service with compliance by matching the depth of their checks to each customer’s risk and explaining those checks in plain terms.
Their customers expect to be known by name. Federal rules still require every institution to verify identities, understand why each account exists, and report suspicious activity.
Smaller institutions can meet both expectations without making a longtime member feel like a suspect or burying a small compliance team in paperwork.
Why Compliance Puts More Pressure on Smaller Institutions
The Bank Secrecy Act (BSA) applies to a $300 million credit union in much the same way it applies to a national bank, but the smaller institution usually has one BSA officer instead of a department.
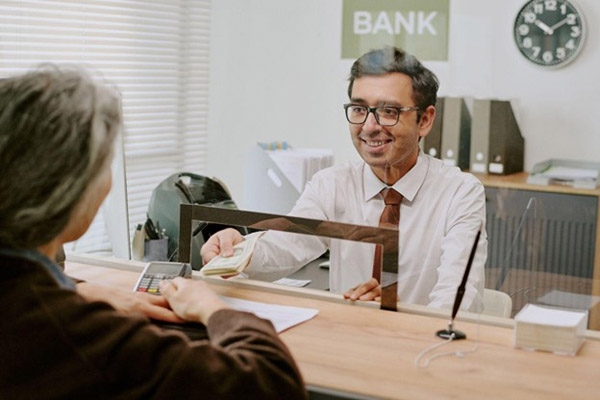
The tellers and lenders who build customer relationships are also the ones collecting IDs, checking documents, and flagging unusual activity, so time spent on manual compliance work is time taken away from serving customers. An employee re-keying ID details into a spreadsheet or running sanctions, checking one name at a time, is not talking to the person at the desk.
For that reason, many community institutions now use a kyc solution to handle document verification and screening, which leaves staff free for the conversation.
How Risk-Based Due Diligence Keeps Low-Risk Customers Moving
Every new customer goes through the customer identification program: the institution collects a name, date of birth, address, and identification number, then verifies them against documents or other sources. Beyond that baseline, regulators expect institutions to scale their due diligence to each customer’s risk.
The Financial Crimes Enforcement Network (FinCEN), the Treasury bureau that writes and enforces Bank Secrecy Act rules, says this directly in its guidance on customer due diligence: an institution can judge a customer’s risk profile to be low and decide it needs no additional information, and it should collect more when the risk is higher.
In practice, a retiree opening a savings account for Social Security deposits gets a short onboarding. A new import business expecting international wires gets more questions about its owners, suppliers, and expected activity.
Why Explaining the Questions Prevents Friction
Customers are more likely to push back on compliance questions when they think they have been singled out.
A business owner asked to name everyone who owns 25% or more of the company, plus one person who controls it, will cooperate more readily when the banker explains that federal law requires the same information from every business customer.
Short, consistent explanations help, and so does telling customers what the information is used for and how it is protected.
The personal touch that keeps customers coming back applies here too: a quick phone call before a document request lets the customer ask questions before the paperwork arrives.
How to Avoid Asking Customers for the Same Information Twice
Loyal customers notice when they are asked for the same documents more than once. This often happens when the deposit, lending, and business banking teams each keep their own records, so a business owner ends up proving who owns the company to each team.
One shared customer profile that every team can see cuts out most of those repeat requests. Since February 2026, FinCEN has also let institutions skip re-checking a business’s owners each time it opens a new account, unless something seems off or the institution’s risk rules call for a new check.
FinCEN does not require customer information to be updated on a set schedule. Instead, an institution updates a customer’s records when it spots a relevant change. That might be a new business partner, a new line of business, or a big jump in how much money moves through the account. Updating only when something changes saves customers from filling out the same form every year.
How Frontline Relationships Strengthen Monitoring
Knowing customers personally becomes a compliance advantage when staff know what to do with what they notice. A teller who sees a longtime member suddenly withdrawing large amounts of cash, or wiring savings to someone they met online, may be watching a scam in progress.
Monitoring software flags unusual transaction patterns, while a teller is the one who notices that a customer seems anxious or is being coached over the phone.
Institutions get the most from this knowledge when they give frontline employees a simple way to escalate concerns to the BSA officer and train them on the common warning signs of elder financial exploitation and other fraud.
Why Compliance Belongs in Broader Risk Planning
Federal rules require every BSA program to have five parts. The institution needs written rules and checks for its staff to follow, regular reviews by someone outside the compliance team, a named BSA officer, ongoing staff training, and customer checks that match each customer’s level of risk.
Leaders should look at these parts alongside the institution’s other big risks, such as bad loans, running short on cash, and cyberattacks. Reviewing everything together as part of enterprise risk management shows where the institution is short on staff or tools. Those gaps are often what regulators point out during an exam.
The same review helps with budget decisions. Leaders can compare the cost of better tools with the cost of a regulator’s penalty or a customer who leaves.
Bringing Service and Compliance Together
The institutions that handle this well spend their compliance effort where the risk is and automate routine checks so staff have time to explain what they ask for.
Low-risk customers get through onboarding quickly, and staff keep the time and personal knowledge that higher-risk relationships need.